The ISO/IEC 27000 family of standards focuses on information security management. It provides frameworks and guidance to help organisations protect information assets, manage security risks, and maintain the confidentiality, integrity, and availability of information across business operations.
What is ISO 27001?
ISO/IEC 27001:2022 is an international standard that specifies requirements for an Information Security Management System (ISMS). It helps organisations identify information security risks, implement appropriate controls, and continually improve the protection of sensitive business and customer information.
What is an Information Security Management System?
An Information Security Management System is a structured framework for managing information security risks through policies, procedures, risk assessments, security controls, monitoring, and continual improvement. It helps organisations protect information in digital, physical, and other relevant forms.
ISO 27001 uses a risk-based approach to information security. Organisations determine the controls needed for their circumstances and document their decisions through the risk treatment process and Statement of Applicability.
Key Principles of Information Security
These principles support the protection of information assets and help organisations establish consistent information security management practices.
Confidentiality
Information Integrity
Information Availability
Risk Assessment
Access Control
Incident Management
Continual Improvement
Who is ISO 27001 for?
ISO 27001 is suitable for organisations of all sizes and sectors, including IT companies, software developers, financial services, healthcare providers, educational institutions, manufacturers, consultants, and cloud service providers. It is particularly relevant to organisations that handle confidential, personal, commercial, or other sensitive information.
How will it benefit my business?
- Improve the protection of confidential and sensitive information.
- Identify, assess, and treat information security risks.
- Strengthen access controls and security responsibilities.
- Improve preparedness for information security incidents.
- Support business continuity and information availability.
- Help address applicable information security obligations.
- Build customer and stakeholder confidence in security practices.
ISO 27001: Benefits
An effective Information Security Management System helps organisations identify critical information assets, evaluate threats and vulnerabilities, and implement risk-based security controls. It supports consistent security practices, incident response, supplier security management, and the review of information security performance.
ISO 27001 certification can demonstrate that an organisation's Information Security Management System has been assessed against the applicable standard. It does not guarantee that security incidents will never occur; its effectiveness depends on implementation, monitoring, and continual improvement.
Should I be certified to ISO 27001?
Certification may benefit organisations that manage sensitive information or provide technology, cloud, financial, healthcare, and professional services. Customers, business partners, and procurement processes may also require certification as evidence of a structured approach to information security management.
How do I get started with ISO 27001:2022?
Key implementation tips
- Define the scope and boundaries of your Information Security Management System.
- Identify information assets, threats, vulnerabilities, and security risks.
- Establish information security policies and risk acceptance criteria.
- Evaluate risks and prepare a risk treatment plan and Statement of Applicability.
- Implement applicable security controls, procedures, and employee awareness.
- Conduct internal audits, management reviews, and continual improvement activities.
Need further guidance? Contact our team to discuss your information security implementation and certification requirements.
Related Information Security Standards
Related standards and guidance include:
- ISO/IEC 27002 — Information security controls guidance.
- ISO/IEC 27005 — Information security risk management.
- ISO/IEC 27701 — Privacy information management.
- ISO/IEC 27017 — Information security controls for cloud services.
- ISO/IEC 27018 — Protection of personally identifiable information in public clouds.
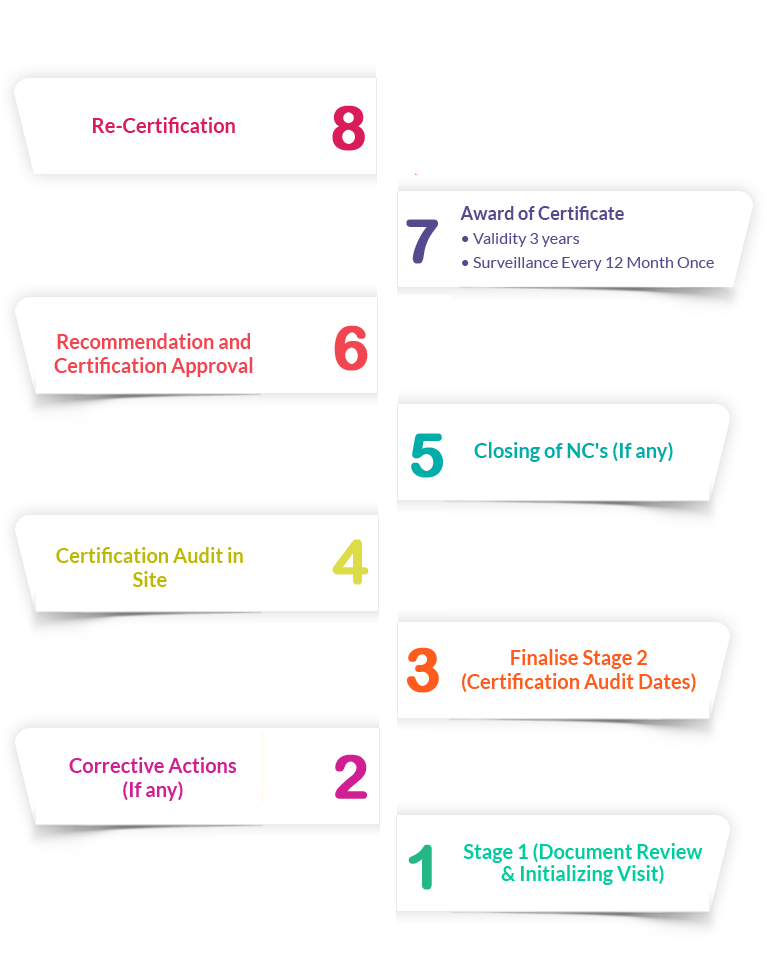
Certification Process
-
01
Preliminary Audit (Optional)
An initial review can identify gaps in information security policies, risk assessments, documentation, and controls before the certification audit.
-
02
Certification Audit
Stage 1 and Stage 2 audits assess readiness, the ISMS scope, risk assessment and treatment, the Statement of Applicability, and the implementation and effectiveness of applicable controls.
-
03
Certification Decision
Following satisfactory audit outcomes and the required certification decision, a certificate may be issued for the approved scope.
-
04
Surveillance Audits
Periodic surveillance audits evaluate whether the Information Security Management System remains effective and continues to meet applicable requirements.
-
05
Recertification
Recertification is completed before expiry in accordance with the applicable certification scheme and audit requirements.